Enterprise AI governance
Govern every AI request.
Give every approved app one policy-controlled inference layer for model access, provider credentials, routing, guardrails, and visibility. Deploy it across macOS, Windows, Linux, and private infrastructure without giving up centralized control.
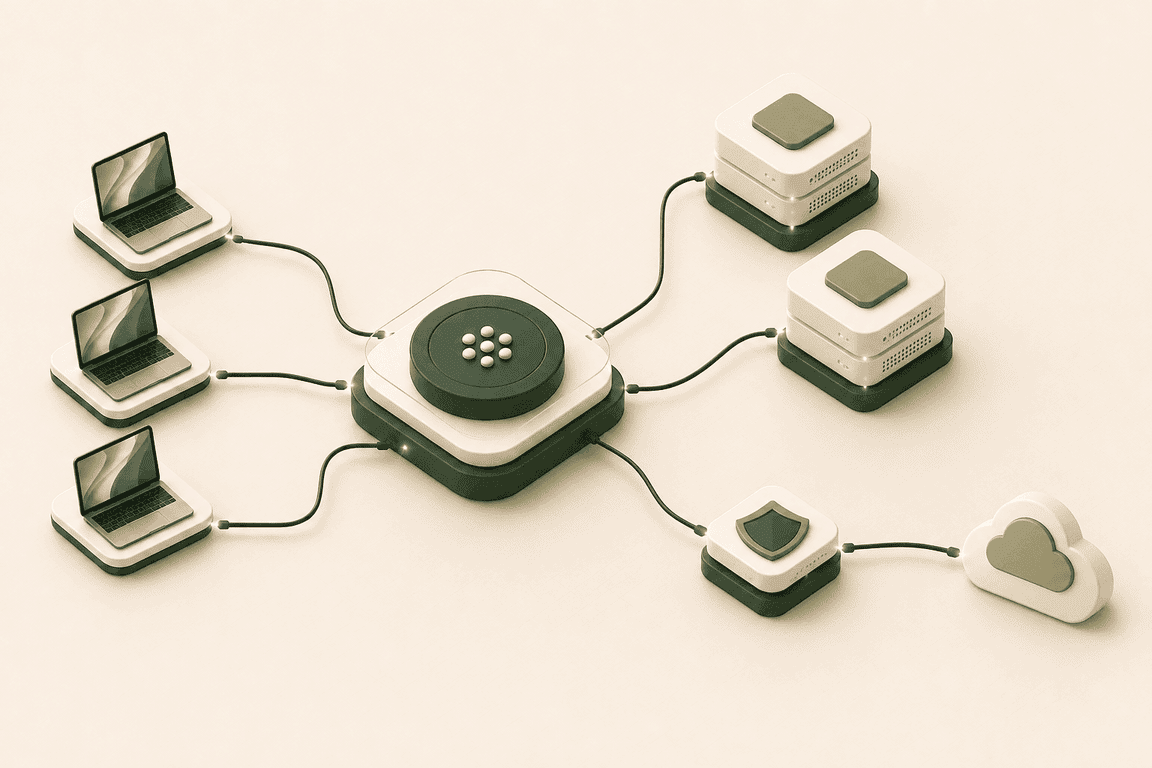
Deployment architecture
Put inference where it makes sense.
Nexus gives your organization one operating model without forcing every workload into the same location. Route work across device, private infrastructure, and cloud based on policy and need.
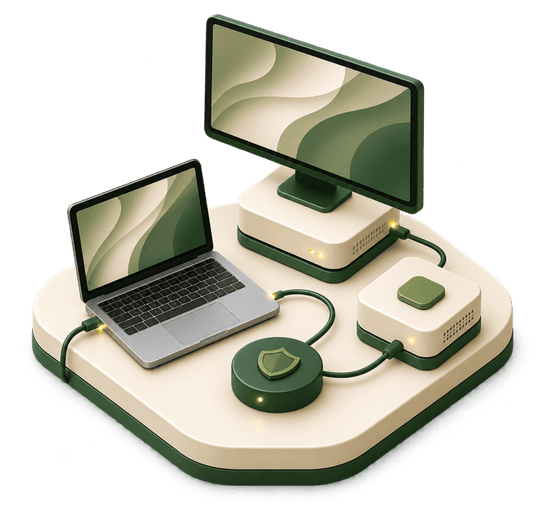
Managed user devices
Run approved local models and give your AI tools one governed endpoint on macOS, Windows, or Linux.
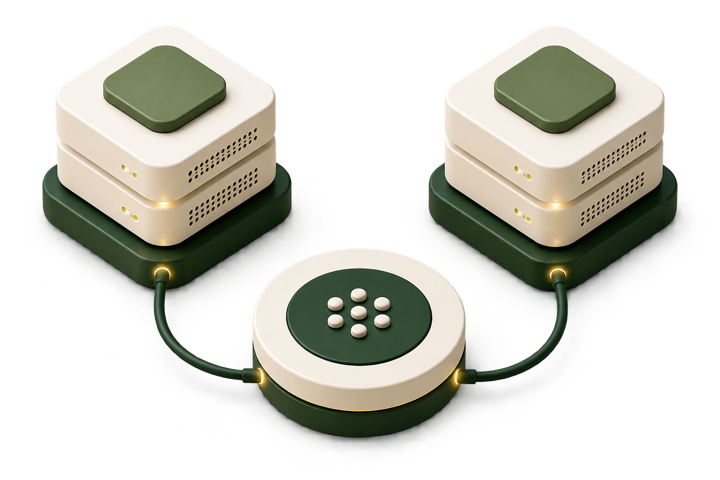
Private AI infrastructure
Operate shared inference on dedicated workstations or servers, balance demand, and control the environment centrally.
Approved provider capacity
Reach selected hosted models through policy-controlled routes without distributing provider keys to endpoints.
MDM + endpoint governance
Make every managed device part of your AI policy boundary.
Use MDM and endpoint-management support to roll out Nexus Runtime across managed macOS, Windows, and Linux devices. Then use Nexus to centralize model access, provider credentials, routing policies, guardrails, and inference visibility. Your teams keep useful local compute while you manage one coherent operating layer.
Talk to Enterprise salesCross-platform fleet rollout
Deploy Nexus Runtime to managed macOS, Windows, and Linux devices through the endpoint-management workflow your IT team already uses.
Policy-aligned configuration
Standardize the Nexus settings and approved access patterns used across employee devices.
Scoped credentials
Use app-scoped tokens instead of sharing provider credentials with every tool.
Team-level visibility
Bring team and user logging, rate limits, and operational ownership into one control plane.
Enterprise controls
Control without constraining where AI can run.
Standardize the access layer while keeping the freedom to use the right infrastructure and model for each workload.
Private and air-gapped
Keep inference and policy enforcement inside environments with strict network boundaries.
Teams and RBAC
Separate administrative responsibility and access by team or role.
SSO
Connect enterprise identity to the Nexus Console and team operations.
Clustered inference
Coordinate supported nodes as shared capacity for larger local model workloads.
Guardrails
Apply PII detection, key blocking, rate limits, and routing policy before requests reach models.
Provider optionality
Combine local, private, and approved cloud models behind stable application endpoints.
Your infrastructure. Your policy.
Design your Nexus deployment with us.
Map your user devices, private inference capacity, governance requirements, and optional provider routes to one Enterprise architecture.
Contact sales